Cookies on fenixpyre.com
We use analytics and marketing cookies to learn how the site is used and to follow up on enquiries. They stay off unless you accept. Privacy policy
DATA SECURITY & PRIVACY RESOURCES
Stay informed on data protection and compliance strategies to help safeguard sensitive information and navigate today’s cybersecurity challenges.
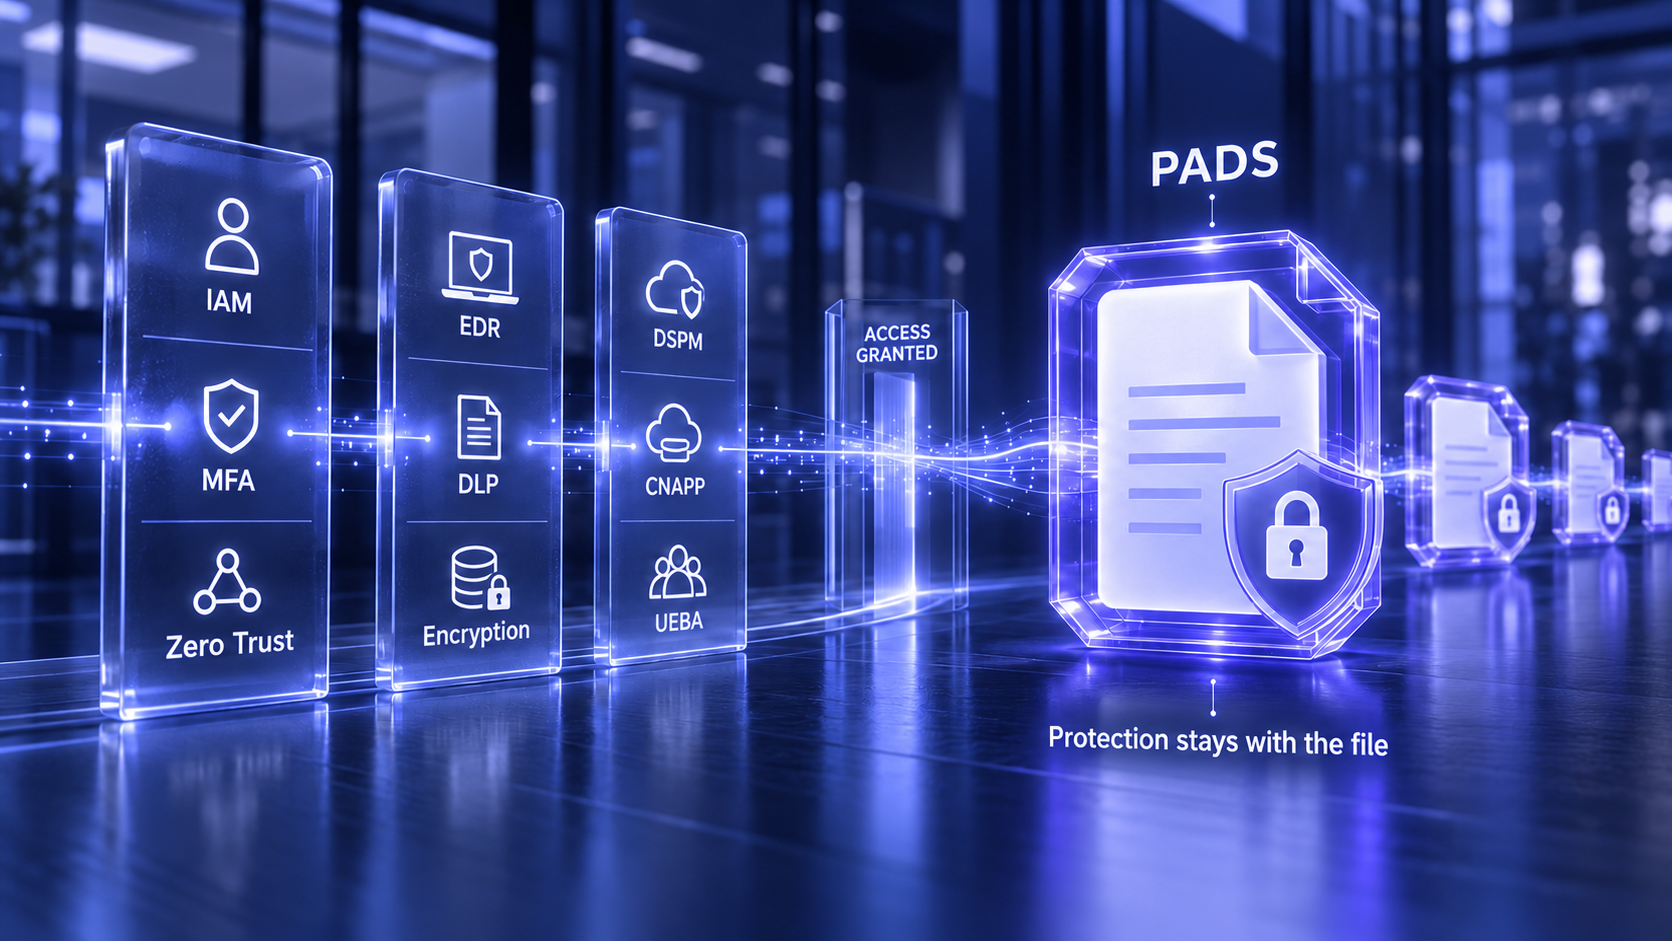
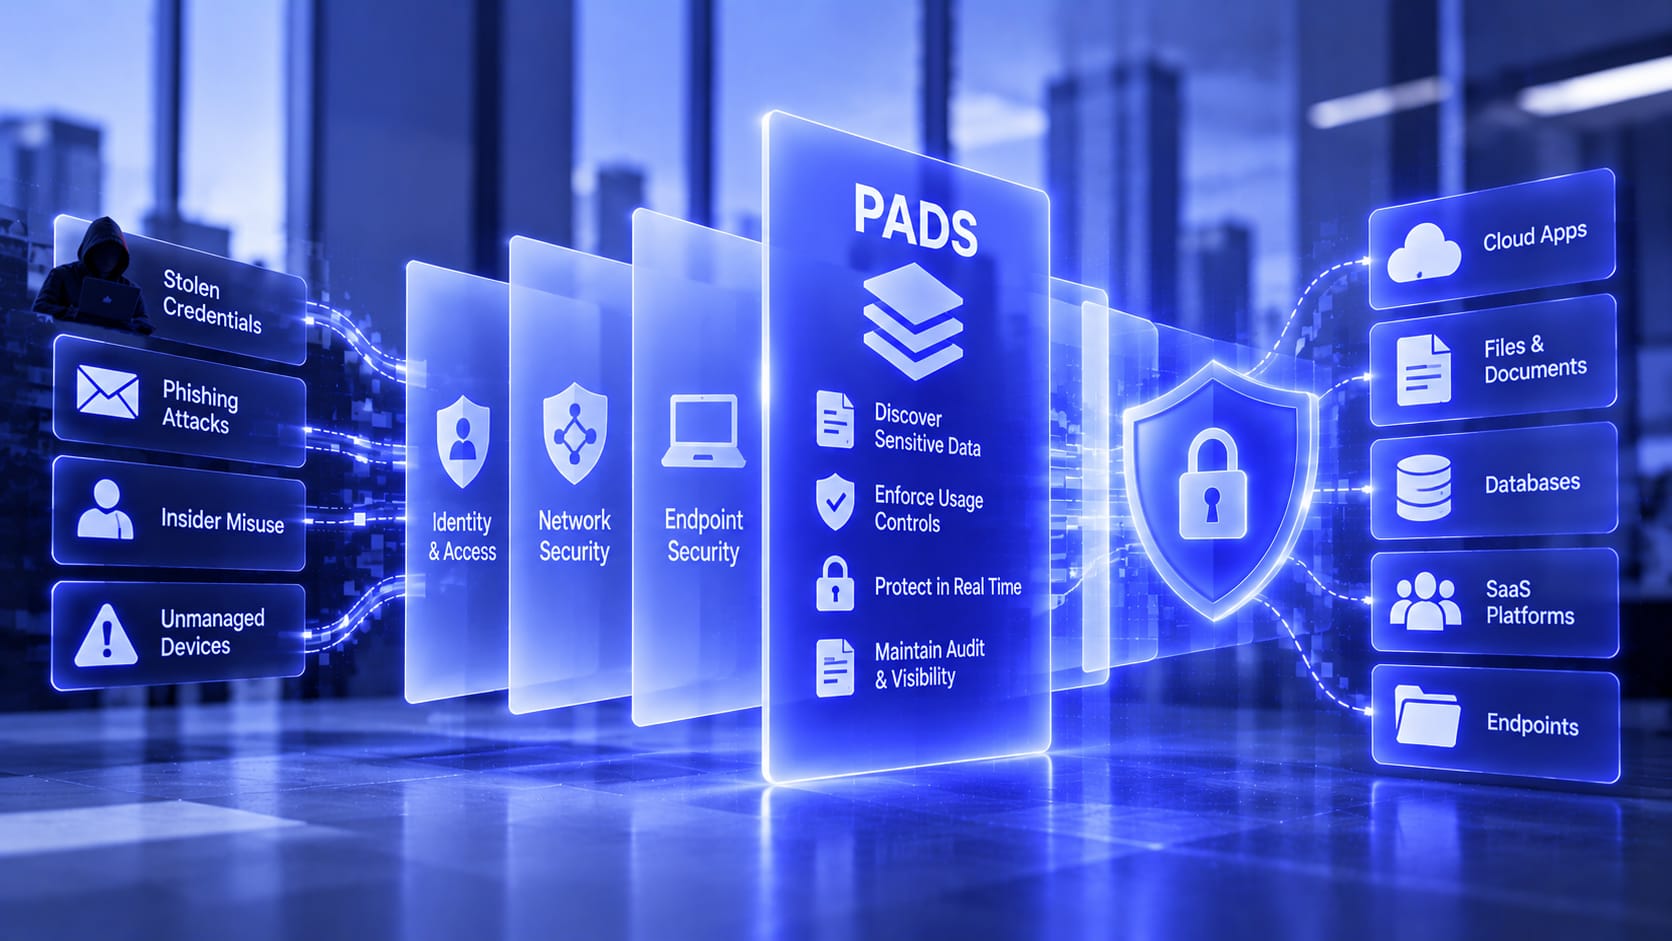
Keep every control. IAM, MFA, Zero Trust, EDR, DLP, and the rest each answer a question about access - here's what each one still needs once access is granted.
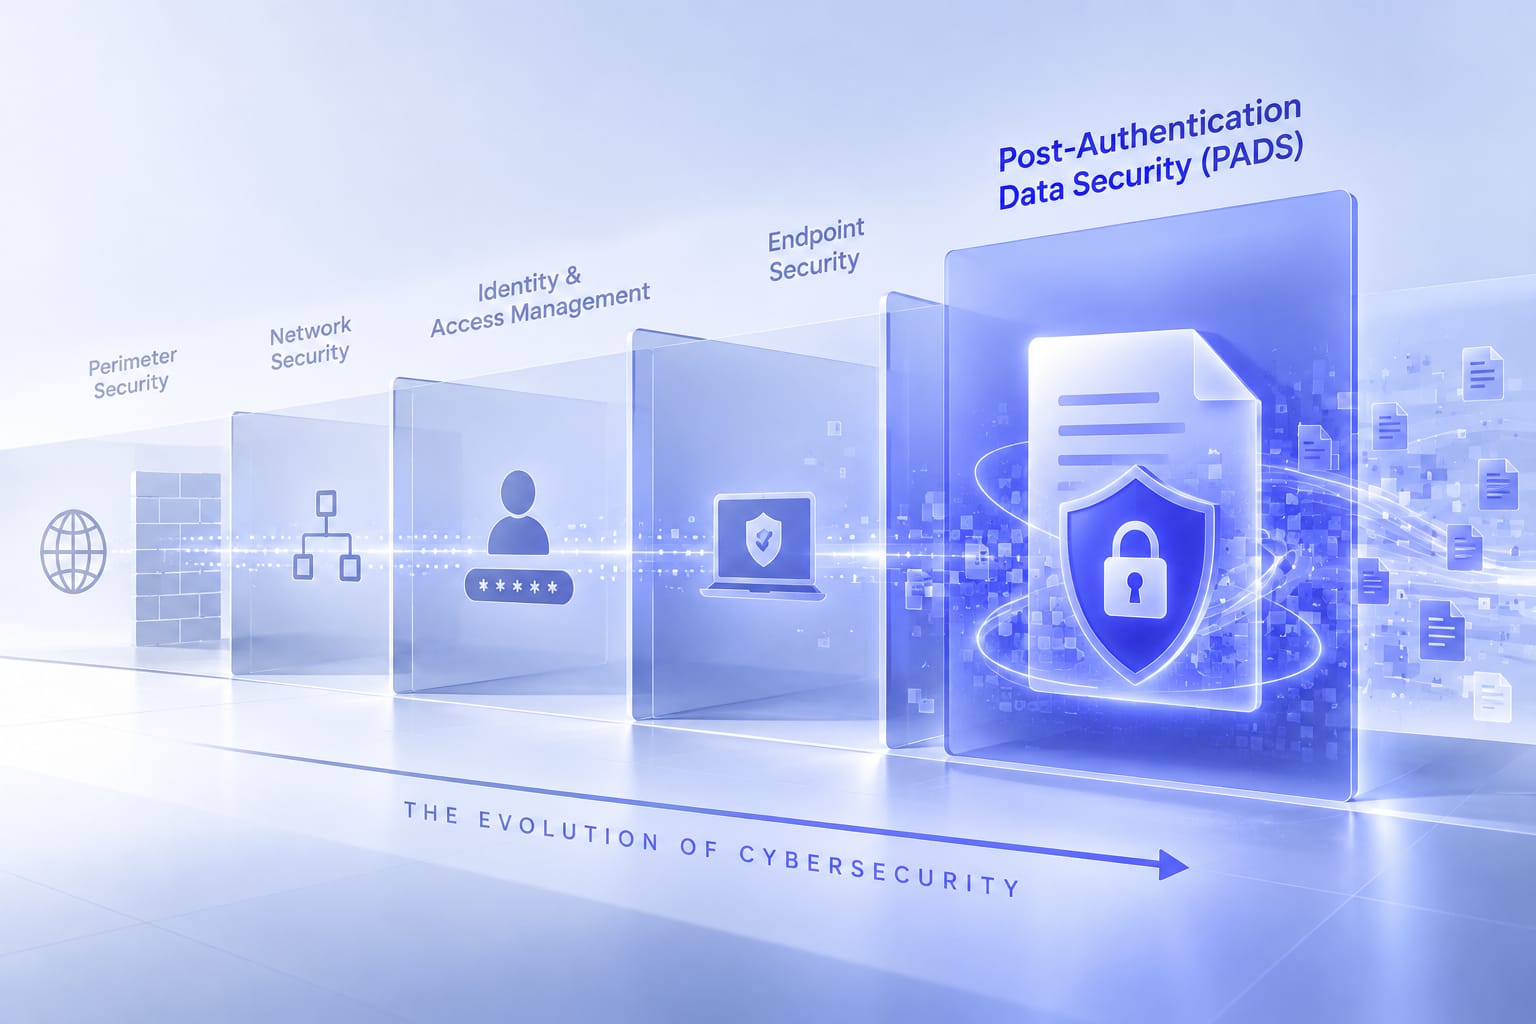
26% of critical vulnerabilities remediated in 2025. The access-layer model has hit its limit. Here is why Post-Access Data Security is the only control that holds when the perimeter fails.
The Mercor breach didn't break authentication - it didn't need to. Every security layer worked as designed - and failed. The missing control isn't better access. It's protecting data after login.
Current litigation focuses on access controls. But most breaches bypass them entirely. The standard of care is measuring the wrong layer.
Accenture reports a 127% surge in insider recruitment on the dark web, exposing a critical gap in data security - and why controlling data use after access is now essential.
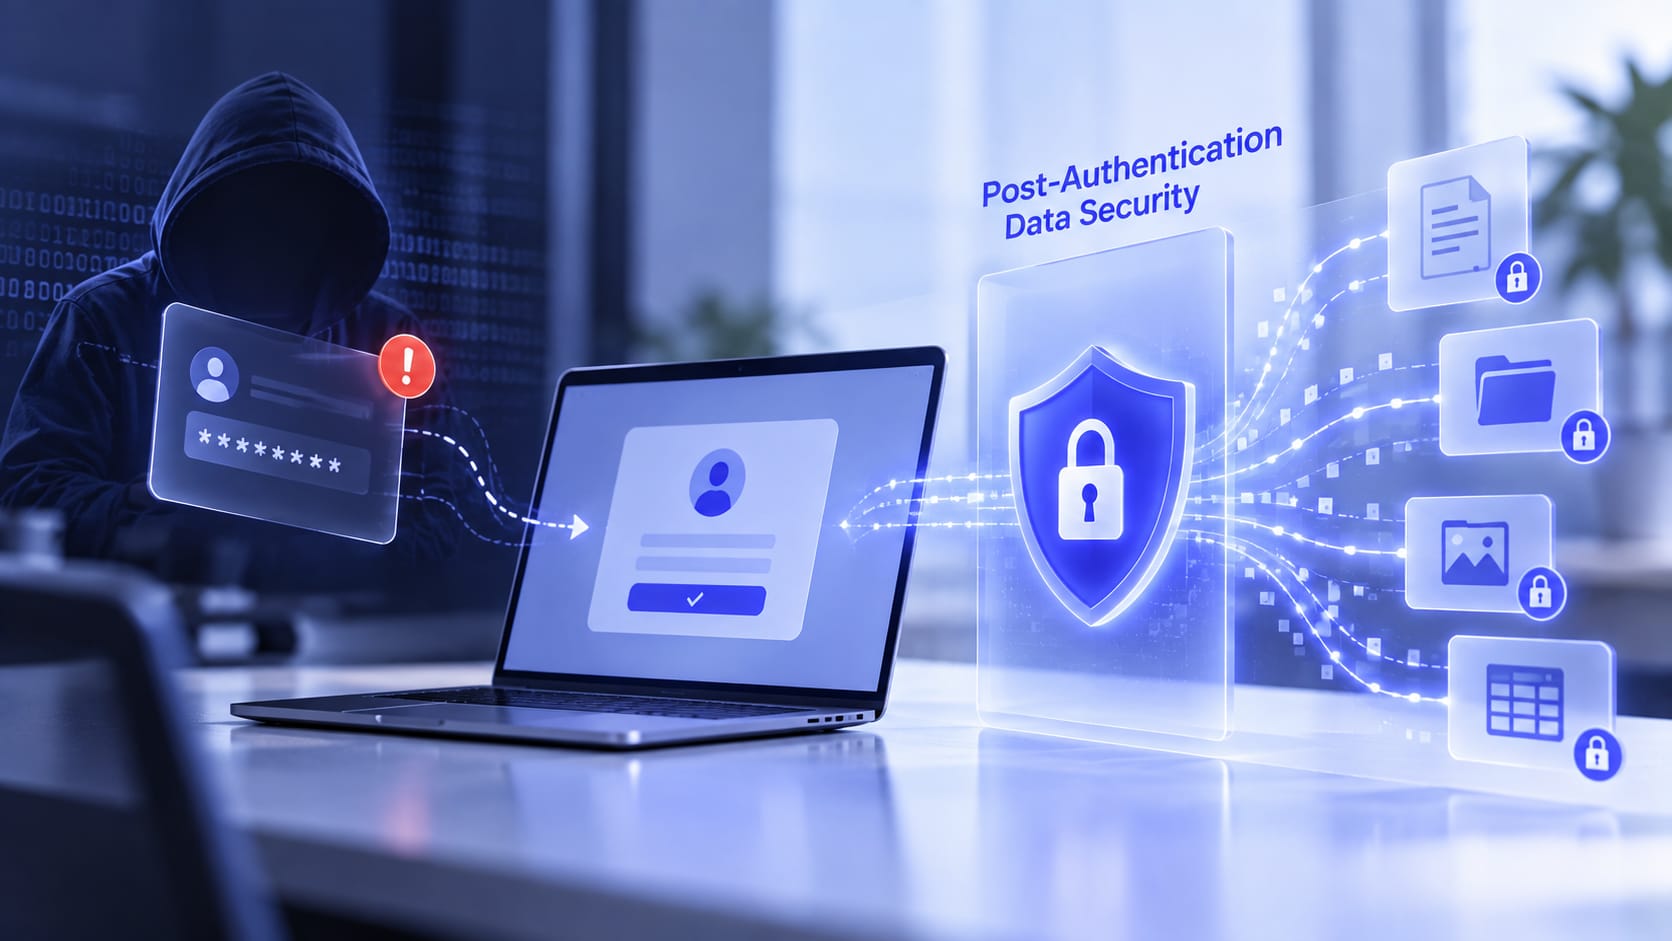
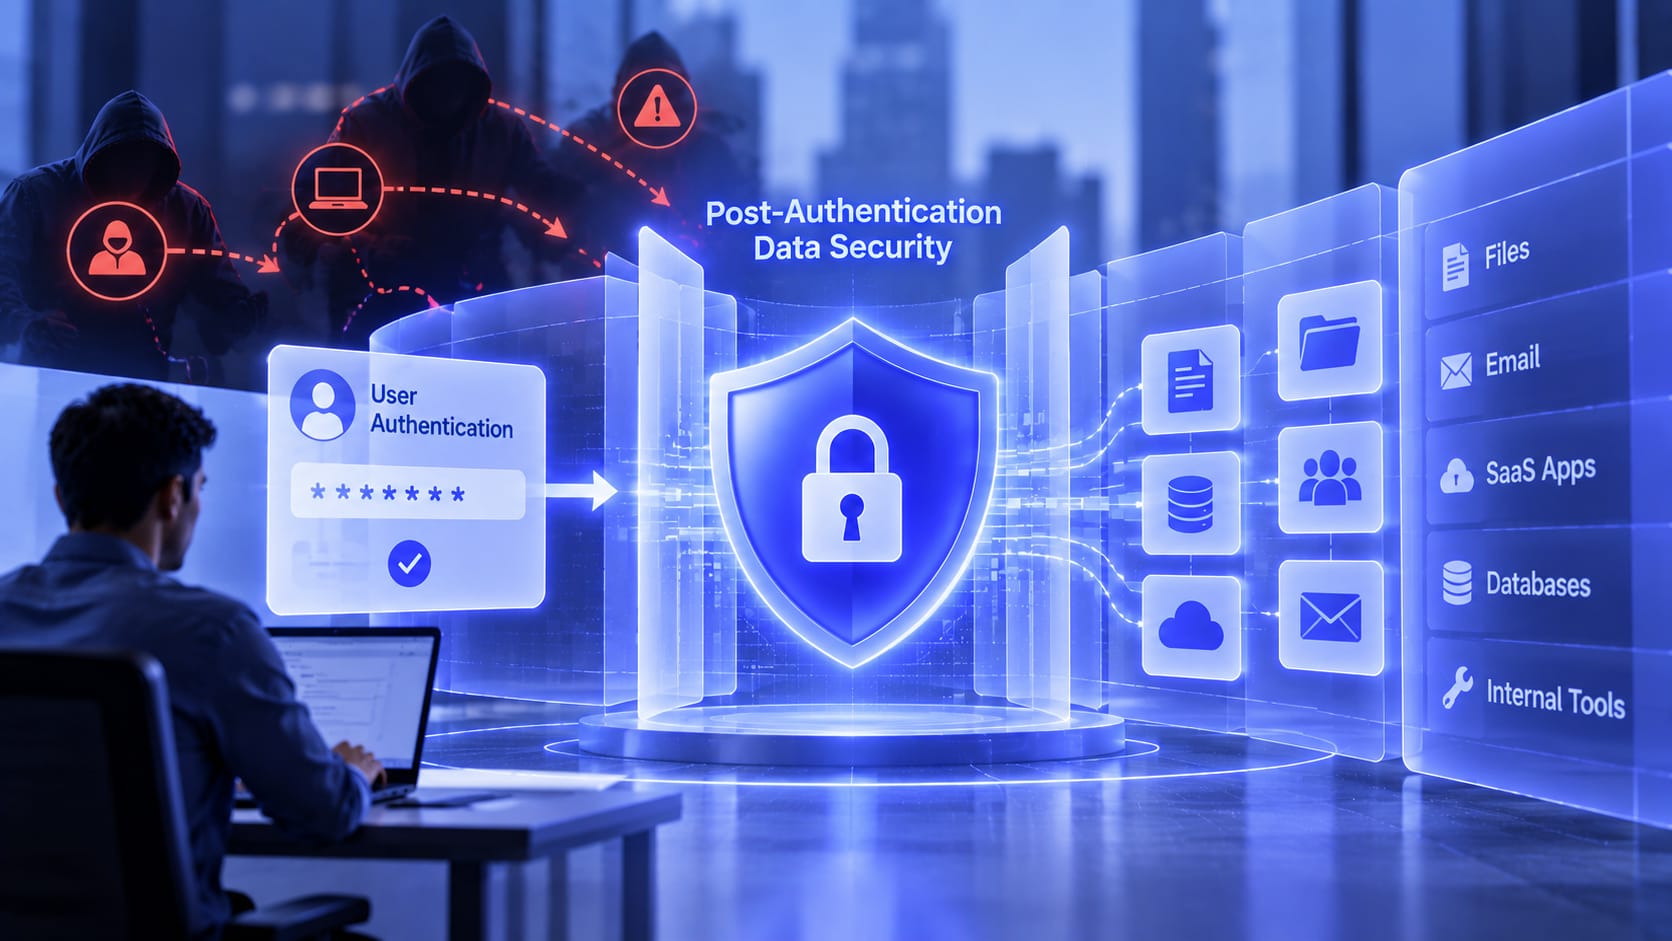
IBM X-Force reveals the real security gap: post-authentication trust. This article explores how valid sessions enable data breaches - and why controlling data use after login is critical.
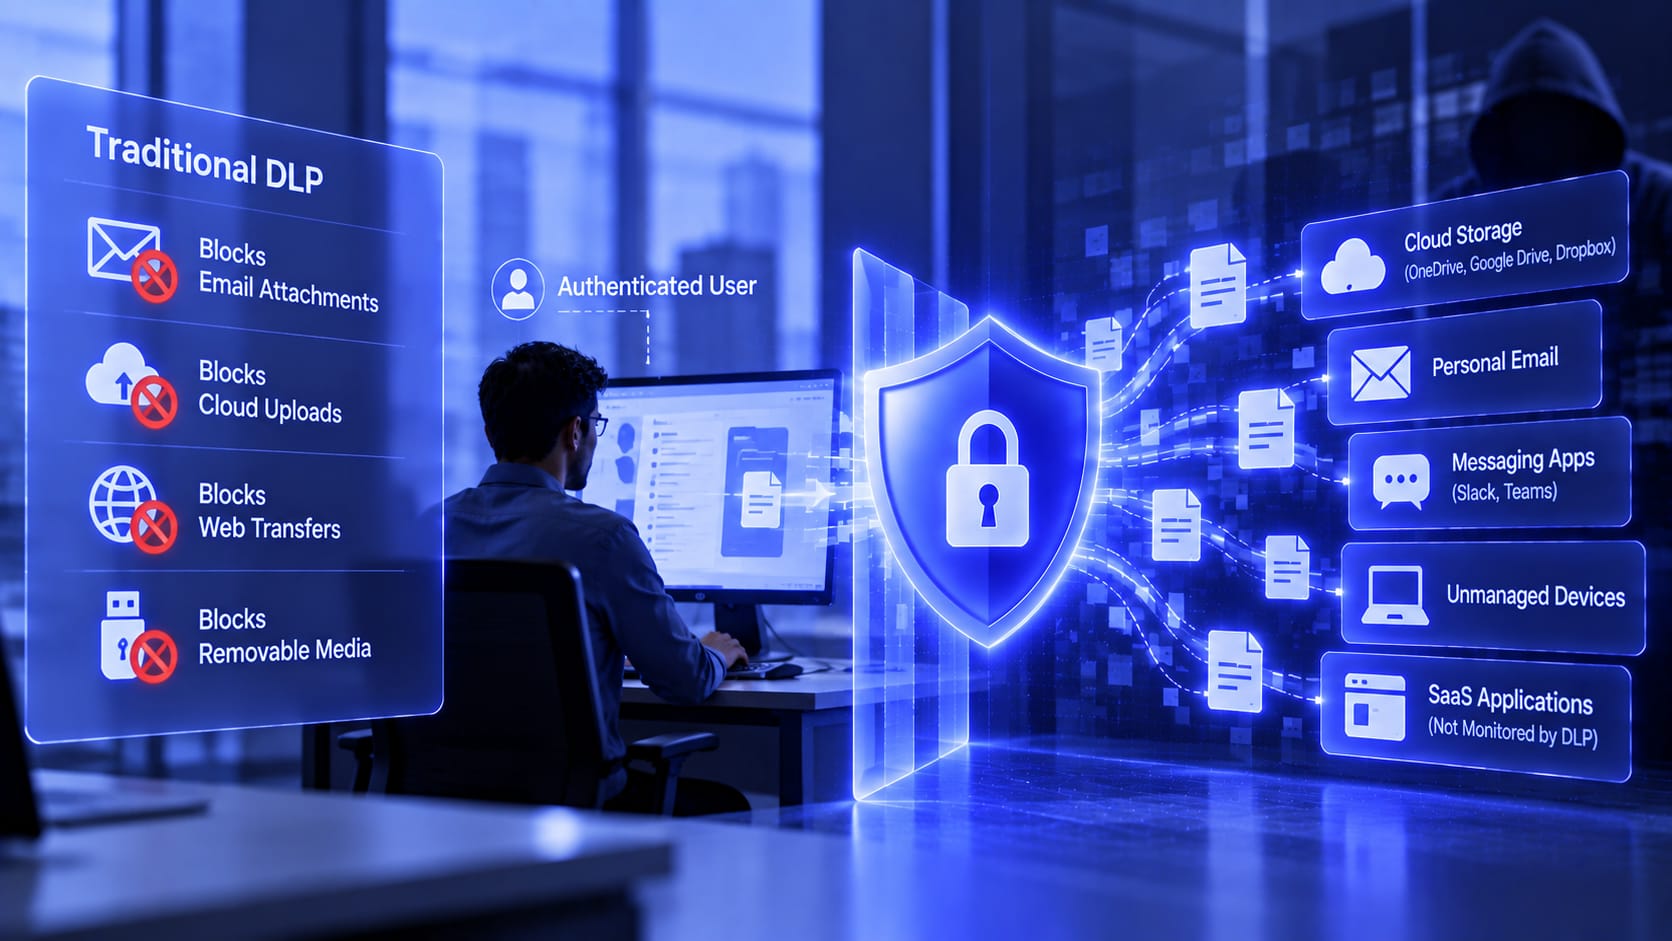
Traditional DLP isn’t broken; it was built for a different era. As attackers use valid credentials, Post-Access Data Security protects data usability, keeping information secure after access.
Zero Trust controls access, not data. Once credentials work, files are exposed. This article explains why breaches happen after login - and why PADS is the missing control.
Phishing wins by stealing identity, not just clicking links. PADS by PostAuth makes phishing irrelevant by keeping data encrypted after login, ensuring stolen credentials never unlock files.
Insiders don't break security; they login. PADS by PostAuth fixes this design flaw by keeping data encrypted after login, ensuring that authorized access doesn't automatically lead to data exposure.
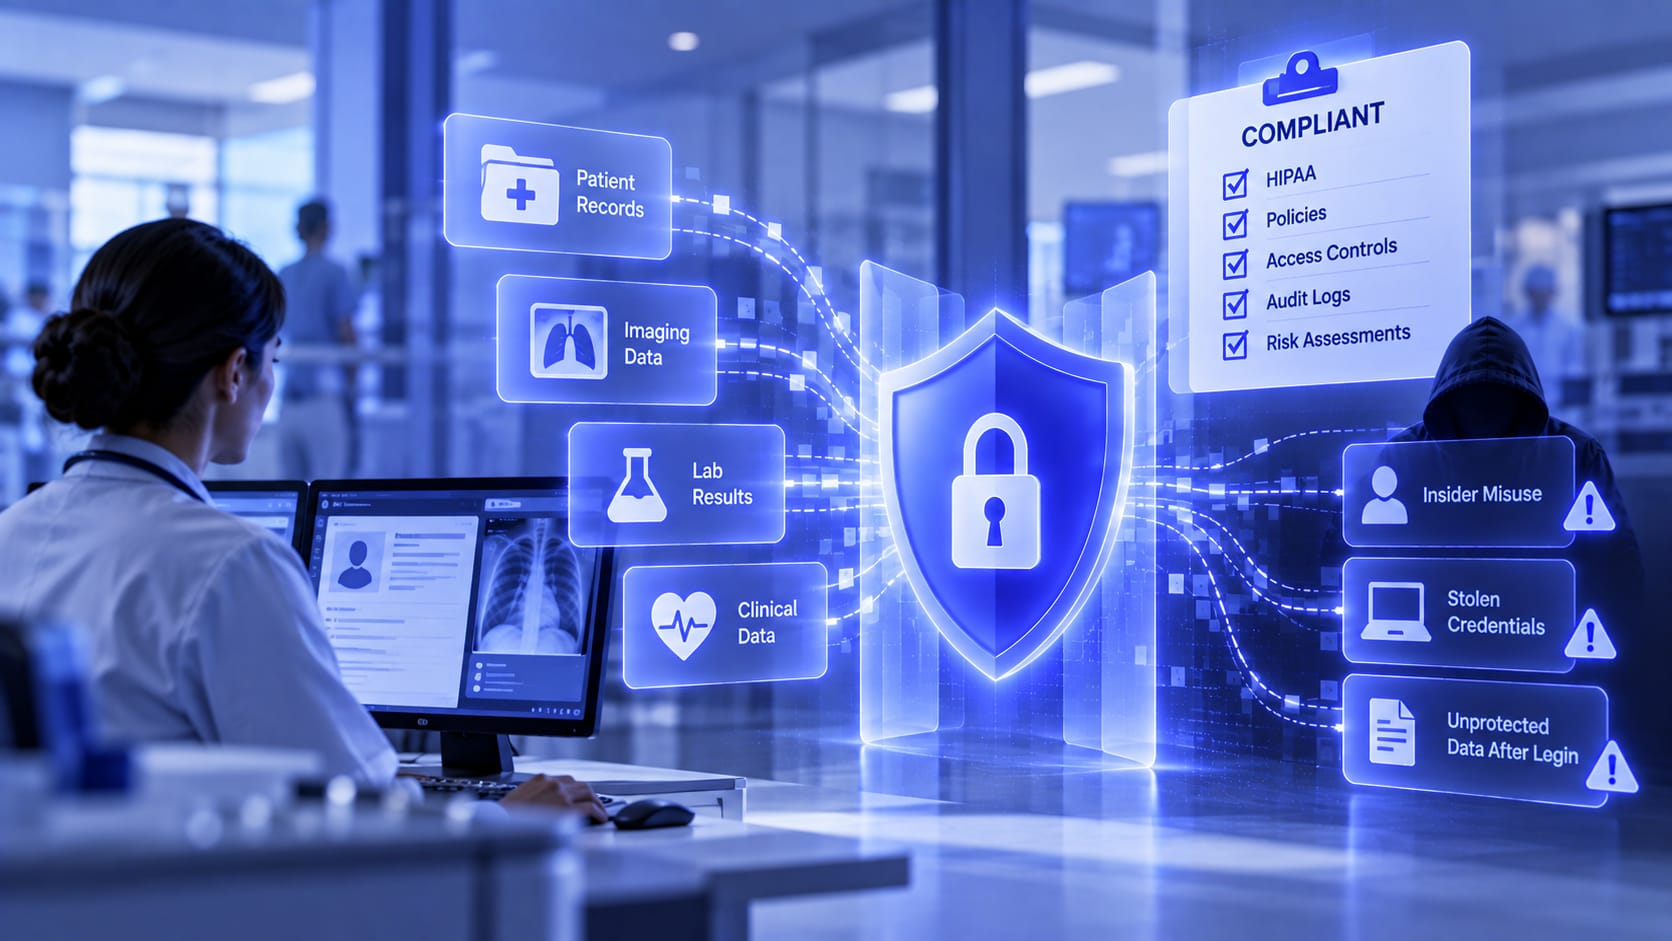
Healthcare is compliant but still leaking. PADS by PostAuth closes the gap by protecting patient data after login, ensuring PHI stays encrypted even when attackers steal valid credentials.
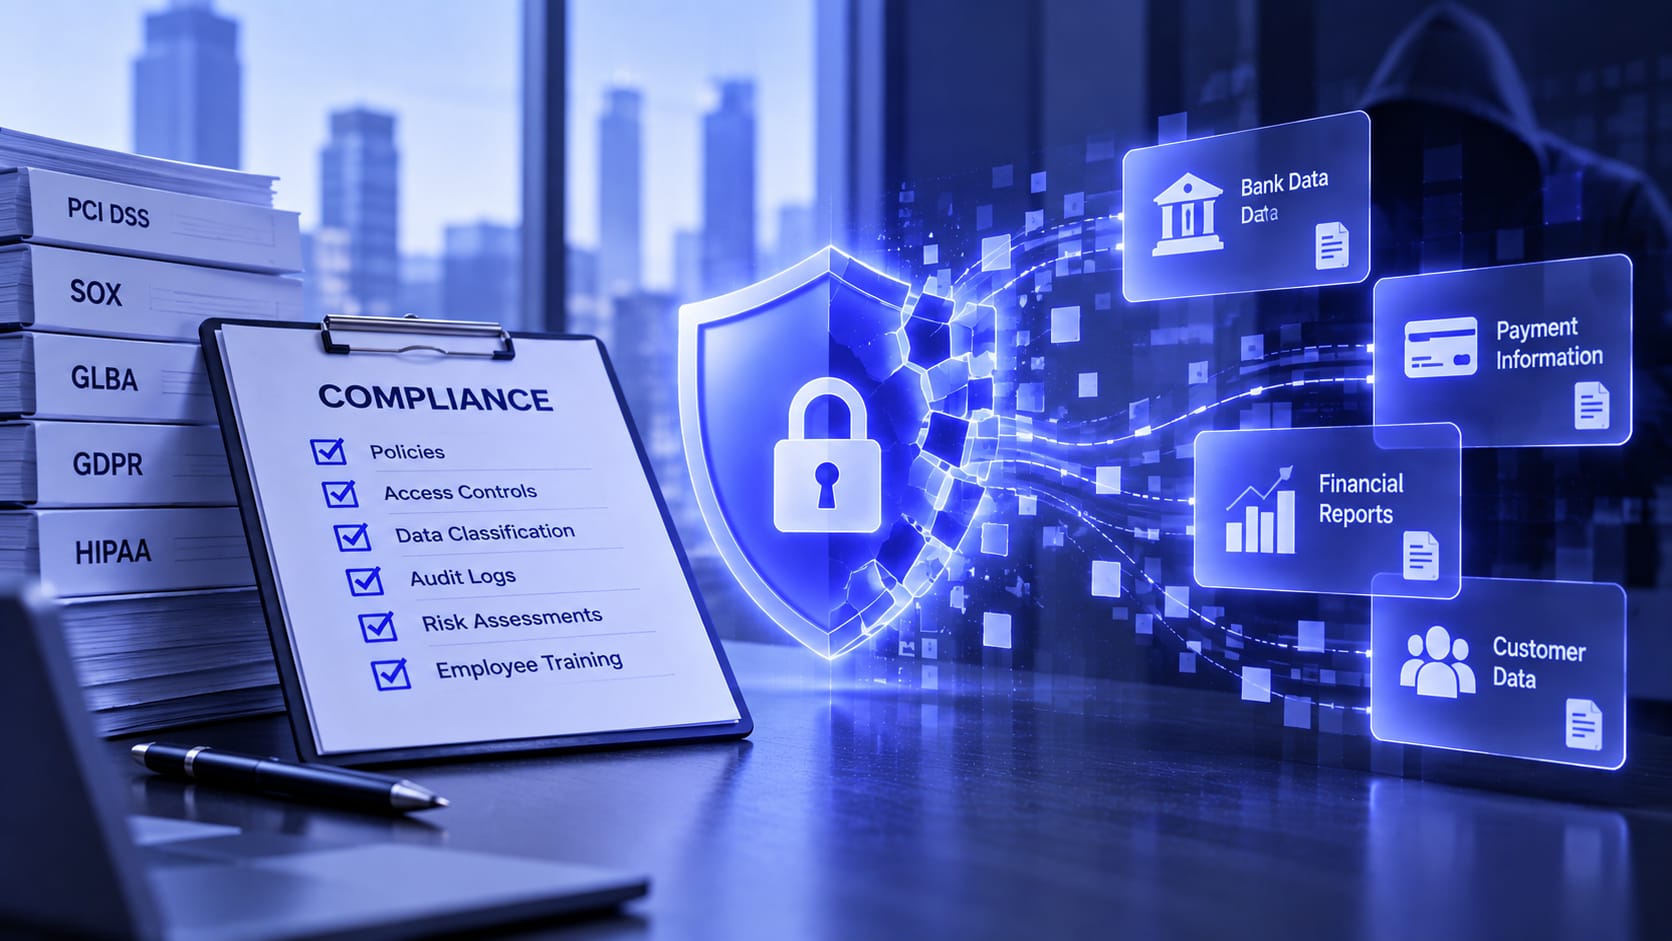
Compliance doesn't stop breaches; most victims were fully compliant when hit. PADS by PostAuth fills the gap by securing data after login, turning regulatory checklists into actual data protection.
Pentests prove systems are hard to break, but ignore that attackers now just log in. PADS closes this gap by securing data at the file level, ensuring that even with valid keys, the data stays safe.
Security spending fails because it only blocks entry, not data loss. Post-Access Data Security (PADS) fixes the ROI by protecting data after login, turning catastrophes into non-events.
Modern breaches don’t break defenses-they log in. When credentials are abused, encryption disengages and data decrypts. PADS protects data after login, where traditional tools fail.
Modern security assumes authenticated users are safe, creating a massive trust gap. Post-Access Data Security (PADS) fixes this by protecting data after login, making stolen logins useless.
Most data breaches occur after attackers gain valid credentials. This article exposes a leadership blind spot in data security and explains why protecting data matters more than perimeter defenses.
Traditional security tools protect networks - not the data itself. This post explains why file-level encryption and true data resiliency are now essential to surviving modern cyberattacks.
Explore how file protection works in the applications your people already use, including when files are shared outside your organization.
Walk through an approved AI request and a blocked one. See where identity, device trust, and access policy shape the outcome.
Map a sensitive file’s journey from creation to sharing, and explore where persistent encryption and access controls fit.