Data Protection
When Accenture Reports a 127% Surge in Dark Web Insider Recruitment, It’s Time to Rethink Data Security
Accenture reports a 127% surge in insider recruitment on the dark web, exposing a critical gap in data security - and why controlling data use after access is now essential.
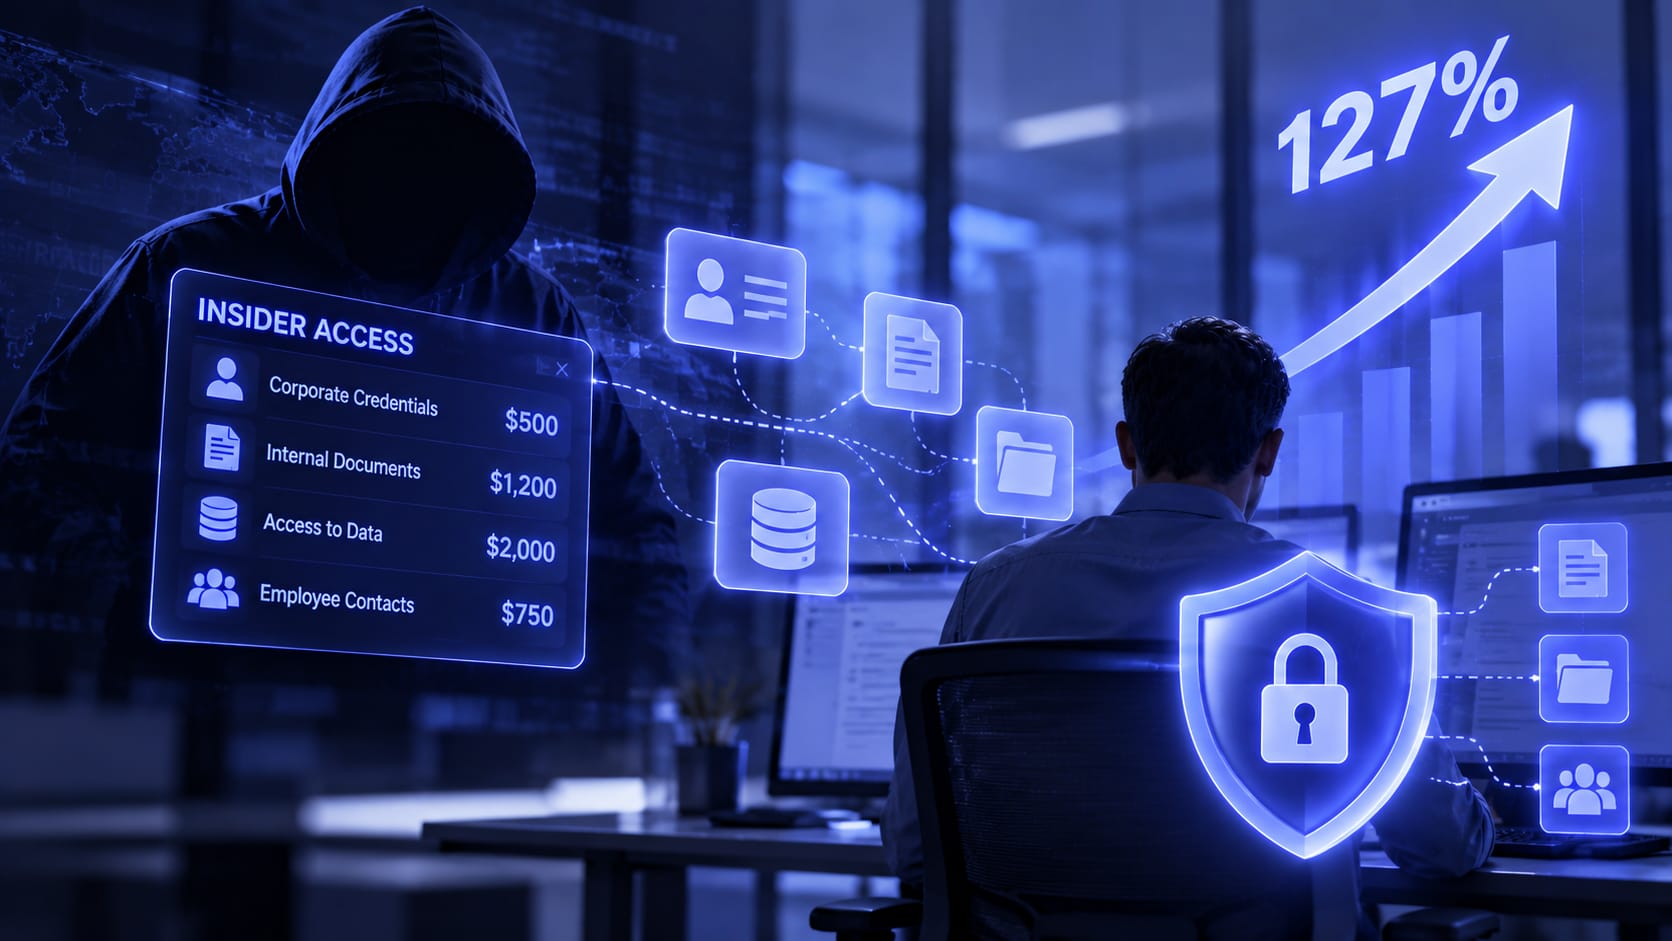
Accenture’s Cyber Intelligence team recently published research that should alarm every CISO and board member: insider threats facilitated through dark web ecosystems are escalating at an unprecedented rate.
The numbers are stark:
- 69% increase in insiders offering access (2025 vs. 2024)
- 127% surge in hackers actively recruiting insiders (vs. 2022)
As Ryan Whelan, Accenture’s Global Head of Cyber Intelligence, explains:
“The insider economy is now principally designed to support early-stage intrusions, with criminal gangs increasingly relying on insiders to bypass cyber defenses.”
This is not theoretical.
Dark web posts explicitly name targets:
- Coinbase
- Binance
- Kraken
- Gemini
- Accenture
- Genpact
- Spotify
- Netflix
…and dozens more across financial services, consulting, and technology.
The going rate?
- $3,000–$15,000 for initial access
- $25,000 for 37 million cryptocurrency exchange records
The Real Implication of Accenture’s Findings
What this research makes clear - when taken to its logical conclusion - is this:
Managing insider risk requires more than governing access. It requires governing how data is used after access is granted.
This is the role of Post-Access Data Security (PADS).
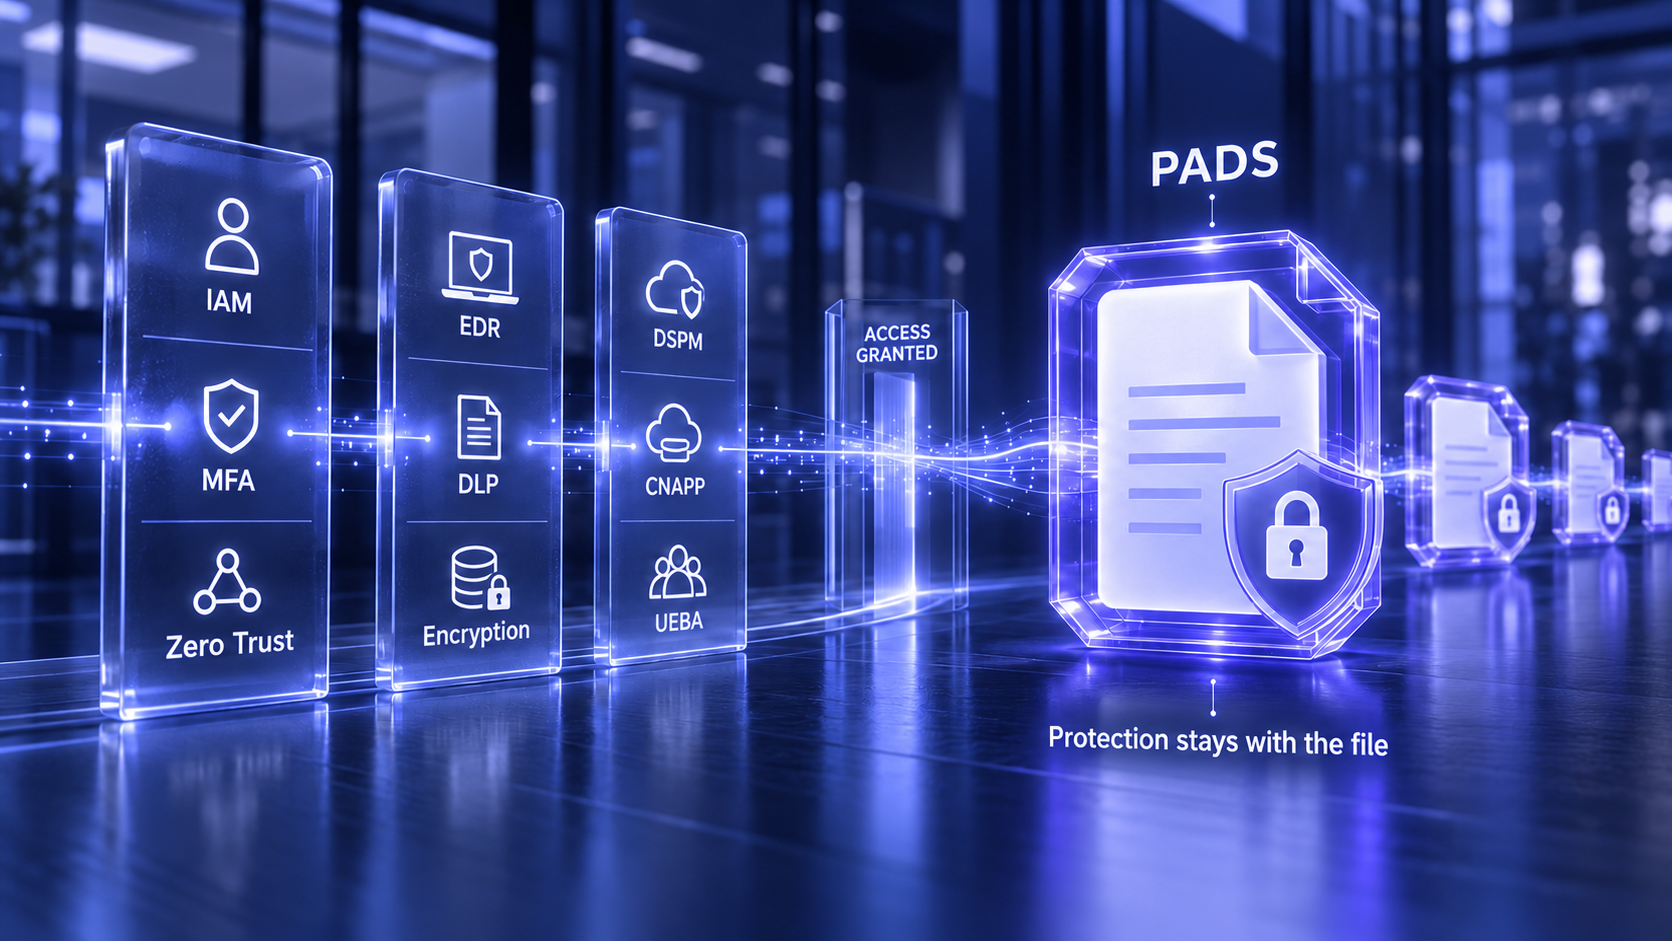
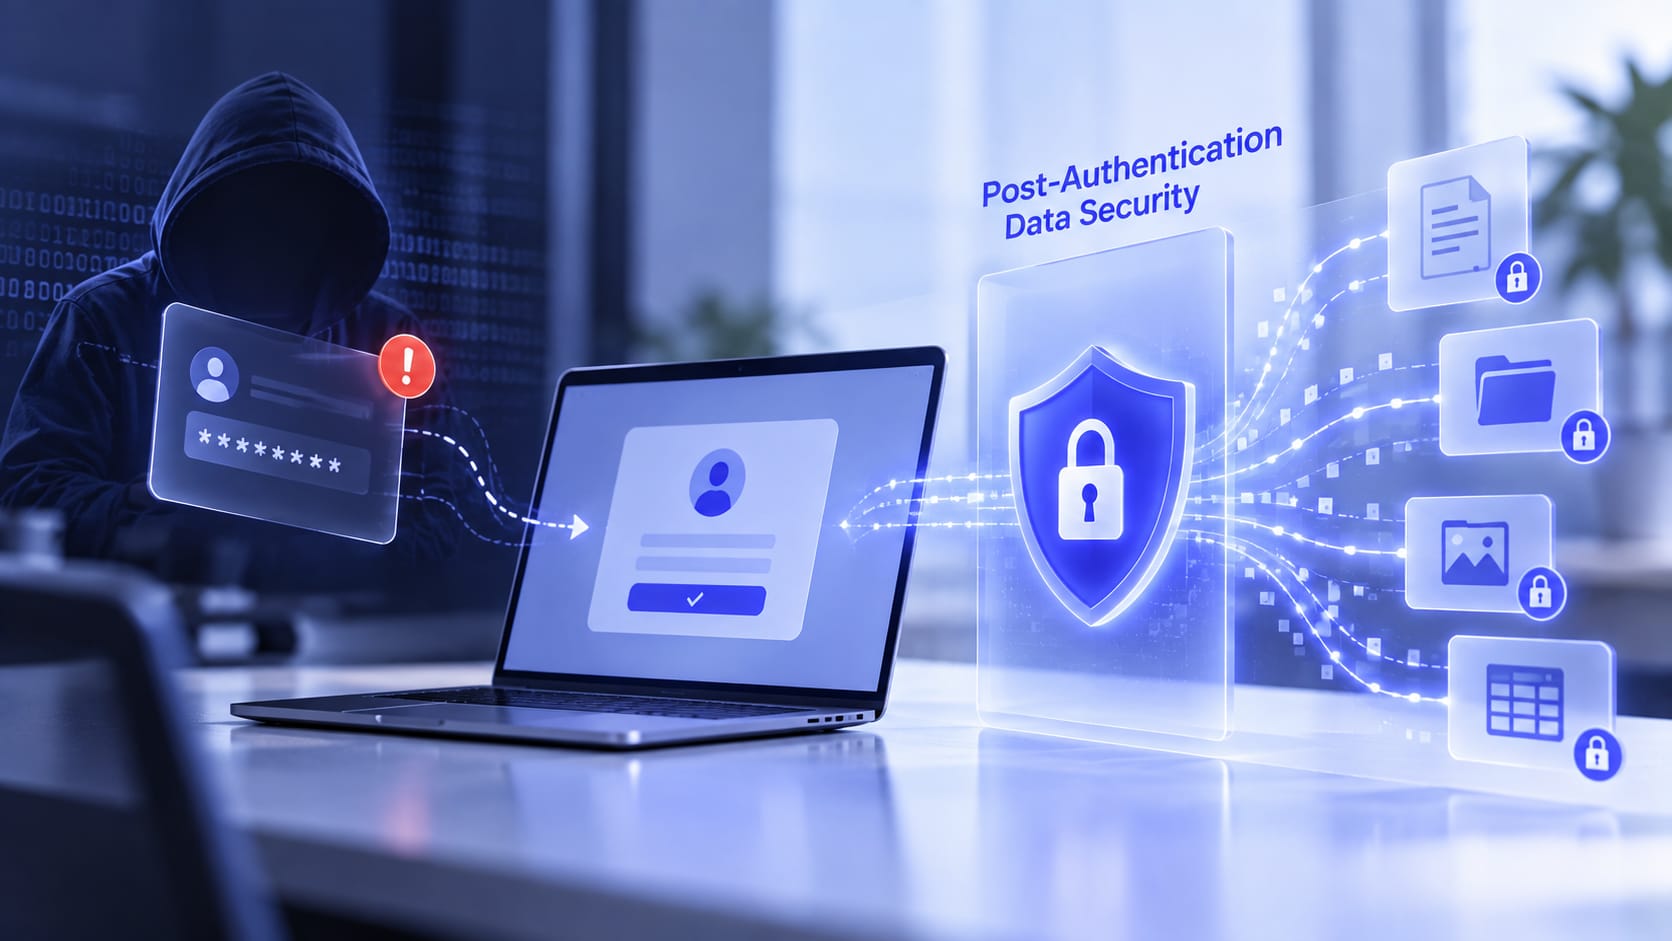
PADS is a security layer that governs how data can be used after access is granted - enforcing policy at the moment of data interaction, not just at authentication.
What Accenture’s Research Makes Clear
Accenture’s findings highlight a structural shift in threat dynamics:
- Insiders provide initial access and credentials (30% of cases)
- Perimeter defenses are bypassed entirely
- Activity appears legitimate - because it is legitimate
- Security controls defer by design once authentication succeeds
Whelan emphasizes lifecycle controls:
- Stronger hiring and identity verification
- Role separation and least privilege
- Immediate access revocation during offboarding
- Monitoring for pre-departure activity
- Behavioral analytics and insider threat programs
These are essential.
They reduce the likelihood that insider threats emerge - or go undetected.
But they also reveal something deeper:
Even with these controls, an authenticated user can still use data in ways that are indistinguishable from legitimate activity.
Where Existing Controls End - and Why the Gap Exists
When a recruited insider acts, the cybersecurity stack behaves exactly as designed:
- Identity is verified
- Access is authorized
- Permissions are correctly applied
- Activity aligns with role expectations
- Monitoring systems observe “normal” behavior
From the system’s perspective:
Everything is working correctly.
And that is precisely the problem.
Because “working correctly” still allows data to be:
- Queried
- Downloaded
- Copied
- Transferred
- Sold
Nothing is bypassed.
Nothing is broken.
No control is technically evaded.
The attack succeeds because:
The security stack is architected to stop at authentication.
Whelan’s findings reinforce this reality:
Attackers are not defeating controls - they are operating within the boundary those controls were designed to trust.
The Architectural Limitation
Modern security is built to answer one question:
Who should have access?
It is not built to answer:
What should an authenticated user be allowed to do with data - right now, in this context?
This is why insider recruitment is so effective.
Existing controls - IAM, Zero Trust, SIEM, DLP, UEBA - are optimized for:
- Preventing unauthorized access
- Detecting abnormal behavior
They are not designed to stop:
Authorized, normal-looking misuse of data
This is not a failure of execution.
It is a limitation of architecture.
The Missing Layer: Post-Access Data Security (PADS)
Accenture’s framework focuses on managing insider risk across the employee lifecycle.
PADS extends that framework into the data interaction lifecycle.
If traditional controls answer:
- Who should have access?
- When should access be granted or revoked?
- Is behavior anomalous?
PADS answers:
- What should this user be able to do with the data they can access?
- Is this specific use of data appropriate in this context?
This is not a replacement for insider threat programs.
It is the layer that ensures their effectiveness - even when insiders act within expected patterns.
Why This Matters in the Insider Economy
The insider recruitment model works because it exploits a core assumption:
Authenticated access implies legitimate use.
Accenture’s research shows attackers are deliberately targeting that assumption.
They recruit insiders because:
- Access is already granted
- Activity blends into normal workflows
- Detection becomes significantly harder
PADS shifts control from access → to data usage.
What Changes When Data Is Governed After Access
In a PADS-enabled environment:
- Access still functions as designed
- Authorized users still perform legitimate work
But:
- Bulk extraction can be restricted or challenged
- Sensitive data use can trigger contextual controls
- Data remains protected - even outside the system
- Actions - not just identities - are evaluated in real time
This means even if:
- An insider is recruited
- Credentials are valid
- Behavior appears normal
The outcome changes.
Data is no longer freely extractable and usable simply because access was granted.
Aligning With Accenture’s Recommendations - And Extending Them
Whelan’s recommendations create a strong foundation:
- Strengthen hiring and identity verification
- Enforce role separation and least privilege
- Revoke access immediately during offboarding
- Monitor for behavioral anomalies
- Expand insider threat intelligence
All of these aim to:
Prevent trusted individuals from using legitimate access to cause harm
But traditional implementations approach this indirectly.
They:
- Limit access scope
- Attempt to detect misuse
- Reduce opportunity over time
They do not directly control:
What happens to data at the moment it is used
Where Traditional Controls Fall Short
| Objective | Traditional Approach | Limitation |
|---|---|---|
| Prevent malicious insiders | Pre-employment screening | Cannot prevent post-hire recruitment |
| Limit exposure | RBAC / PoLP | Broad access still exists within roles |
| Stop access at risk | Offboarding | Reactive - after decision point |
| Detect misuse | UEBA / monitoring | Requires deviation from “normal” |
| Identify targeting | Threat intelligence | Does not stop insider action |
These controls rely on:
- Predicting intent
- Detecting anomalies
- Acting after signals appear
In insider recruitment scenarios:
Those signals may never appear in time.
How PADS Delivers the Outcome Directly
| Objective | PADS Capability | Outcome |
|---|---|---|
| Limit insider impact | Data usability governance | Controls actions within valid access |
| Prevent extraction | Contextual policy enforcement | Evaluates intent at time of use |
| Reduce detection reliance | Real-time controls | No need for “abnormal” behavior |
| Mitigate insider risk | Persistent data protection | Exfiltrated data is unusable |
| Contain breaches | Outcome-based enforcement | Prevents usable data loss |
PADS operates where risk actually materializes:
The moment data is accessed and used
The Strategic Implication: An Architectural Fault Line
Accenture classifies insider threats as a medium-frequency, high-impact strategic risk.
But the deeper implication is this:
Insider risk is not an edge case - it is a consequence of how cybersecurity is designed.
Whelan’s findings expose a critical assumption:
Once a user is authenticated, risk is sufficiently managed.
That assumption no longer holds.
Modern architecture treats:
- Authentication as the boundary of trust
Everything beyond that boundary is governed by:
- Permissions
- Expected behavior
- Post-event detection
Not by real-time control of data itself.
This is the fault line.
The Bottom Line
Accenture’s findings don’t just highlight the rise of insider threats - they expose a fundamental flaw in modern cybersecurity:
The assumption that risk ends when access is granted.
In reality:
That is where risk begins.
The Verizon DBIR reinforces this:
- 74% of breaches involve the human element
- Occurring within legitimate, authenticated sessions
No controls are bypassed.
No systems are broken.
Attackers simply operate inside the boundary the stack was designed to trust.
Whelan’s recommendations strengthen identity and access.
But they also point to a deeper truth:
Without governing how data is used after access is granted, the problem remains unsolved.
That is what Post-Access Data Security (PADS) delivers.
It shifts security from:
- Controlling entry
To:
- Controlling outcome
Because in today’s threat landscape:
Access is no longer the boundary of risk. Data usage is.
Resources
- Accenture Cyber Intelligence Report: Insider Threat Escalation (2025)
- What is PADS - The definition, category map, and how PADS completes the security model
- Why PADS now - The forces driving post-authentication data theft
Final Thought
Every employee with access to sensitive data is a recruitment target.
Traditional security stops at authentication.
That’s exactly where the insider economy starts.