Data Protection
The Security Treadmill Is Speeding Up, And Your Data Is Still Exposed
26% of critical vulnerabilities remediated in 2025. The access-layer model has hit its limit. Here is why Post-Access Data Security is the only control that holds when the perimeter fails.
Security teams fully remediated only 26% of critical vulnerabilities in 2025, down from 38% the year before.
After record security investments. After years of vendor promises. After countless board presentations about improving the security posture. Organizations are getting worse at closing the access-layer gaps that the entire current security model depends on closing.
The 2026 Verizon Data Breach Investigations Report, the most authoritative annual analysis of real-world breach data, drawing on more than 22,000 confirmed breaches across 145 countries, describes the remediation gap as potentially reaching “the speed of light”: a theoretical ceiling on how fast organizations can close vulnerabilities regardless of how much they invest.
Read that again. Not a ceiling they haven’t reached yet. A ceiling they may already be hitting.
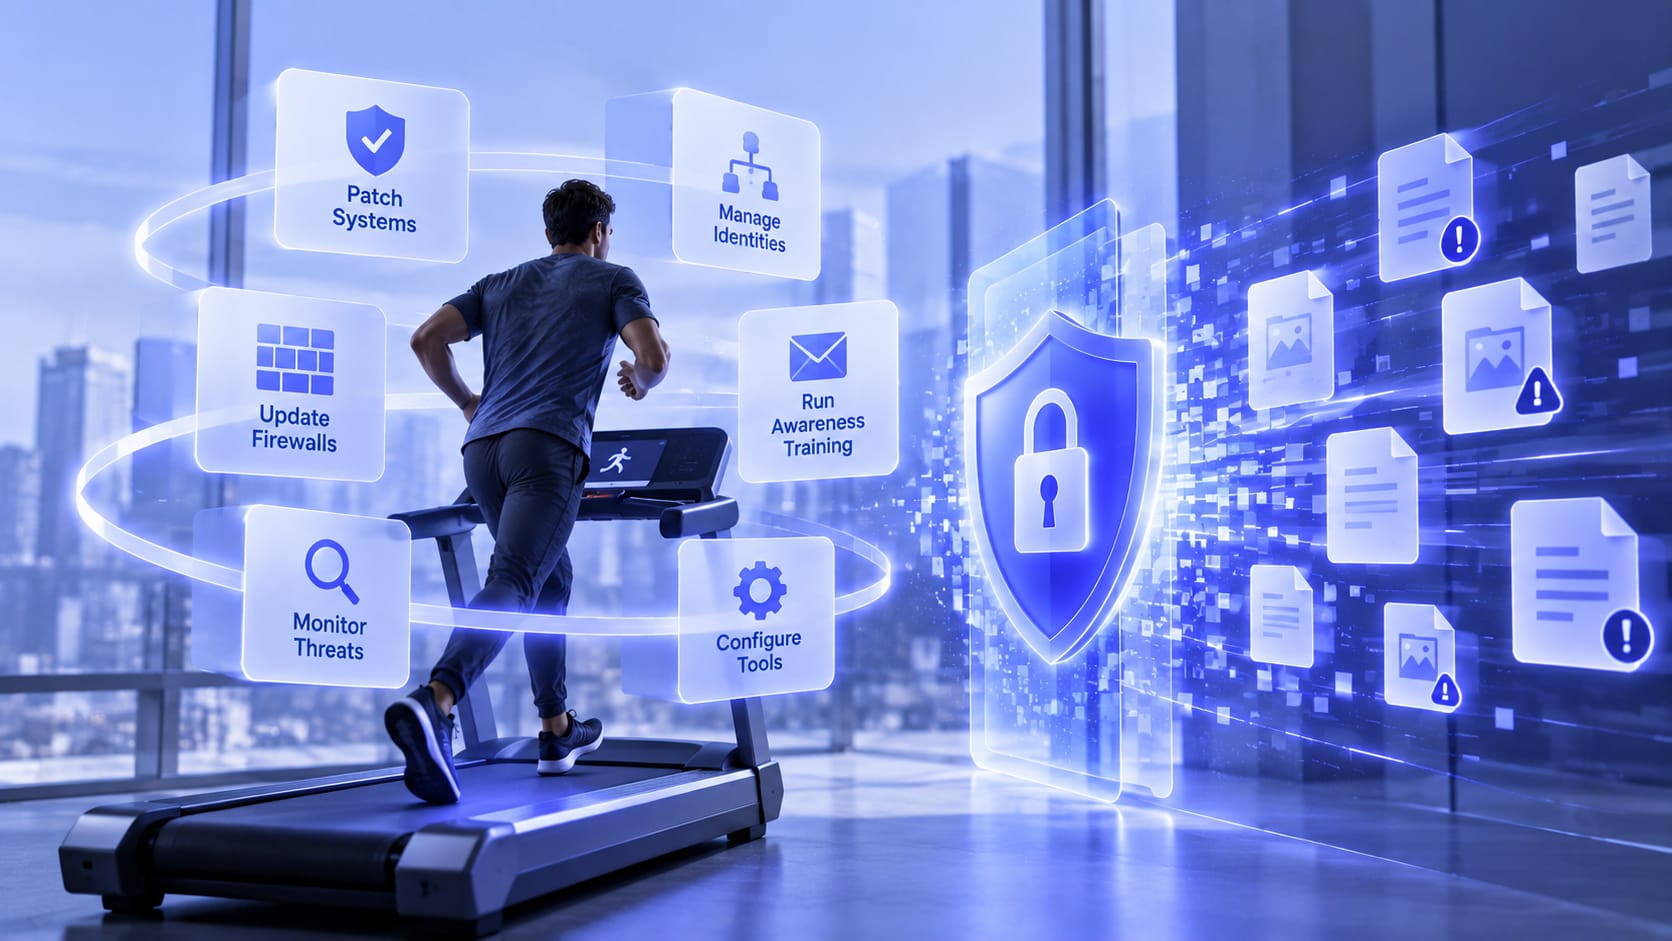
The Treadmill Nobody Talks About
The numbers behind that conclusion are worth examining carefully because they reframe the entire conversation about enterprise security.
In 2025, security teams proactively patched 63.7 million vulnerability instances, a 30% increase from the prior year. More effort. More resources. More investment. And yet the percentage of critical vulnerabilities fully remediated fell from 38% to 26%. The median time to full remediation increased from 32 days to 43 days.
The reason is not negligence. It is arithmetic. The volume of vulnerabilities grew by 50% in a single year. At Day 7, an extraordinarily fast remediation milestone that few organizations consistently achieve, 60 to 70% of critical vulnerabilities remain open regardless of organizational maturity, tooling investment, or mandate pressure. The DBIR’s own analysis suggests this first-week rate has barely moved despite three years of additional process development.
Organizations are running faster and falling further behind simultaneously. The treadmill is speeding up.
Why This Matters Beyond the Patch Queue
Security professionals already know patching is hard. What this data reveals — and what most organizations have not yet absorbed — is that the legal and compliance framework built around access-layer security is resting on a foundation the data proves cannot hold.
Every major compliance framework, NIST, ISO 27001, SOC 2, the FTC’s guidance under Section 5, defines reasonable security in terms of access-layer controls: multi-factor authentication, credential rotation, network segmentation, vulnerability patching. Courts evaluating data breach negligence claims defer to these frameworks as the standard of care.
But that standard of care assumes organizations can maintain access-layer controls at a level sufficient to prevent exploitation. The 2026 DBIR conclusively documents that they cannot, not because of inadequate effort, but because the math has turned against them.
At current remediation rates, 74% of critical vulnerabilities remain open after the first week of detection. Third-party breaches, where organizations have even less control over remediation timelines, now represent 48% of all breaches, up 60% from the prior year. Only 23% of third-party organizations fully remediated missing MFA on their cloud accounts.
The access-layer model is not failing because organizations aren’t trying. It is failing because the attack surface has grown faster than any remediation process can address.
The Attack Chain the Remediation Data Reveals
Here is what makes the remediation finding particularly significant for understanding data exposure.
Vulnerability exploitation has become the leading initial access vector at 31% of breaches, up 55% from the prior year. The instinctive response is to invest more in patching and access controls. But that response misses what the DBIR documents happens after initial access.
Once inside, attackers almost universally proceed to credential harvesting. Password Dumper, the technique of extracting credentials from compromised systems, appears prominently throughout the System Intrusion pattern, which now accounts for 61% of all confirmed breaches. The DBIR documents that within System Intrusion breaches, Use of stolen credentials and Exploit vulnerability are tied at 39% each as action varieties. They are not alternatives. They are sequential steps in the same attack chain.
A vulnerability gets the attacker into the environment. Credentials get the attacker to the data. And the data, in 67% of all breaches, is Internal data: the emails, documents, contracts, reports, and presentations that constitute an organization’s most sensitive unstructured information.
The vulnerability opened the door. The credentials opened the files. And the files were readable because nothing protected them at the file layer.
The Gap the Current Standard Cannot Close
This is the Post-Access Data Security gap — and it exists independently of how well an organization patches its vulnerabilities.
An organization that fully remediates 100% of its critical vulnerabilities, a standard no organization in the DBIR dataset achieves, still faces credential theft through phishing, pretexting, supply chain compromise, and insider misuse. The DBIR confirms the human element is present in 62% of all breaches, and social engineering attacks targeting mobile devices succeed at rates 40% higher than traditional email phishing.
An organization that deploys MFA across every interactive user session, another standard few fully achieve, still leaves non-interactive service accounts, CI/CD pipeline credentials, and API keys exposed. The DBIR notes explicitly that organizations should “pay special attention to service and machine accounts.” These are the credentials that MFA does not and cannot protect.
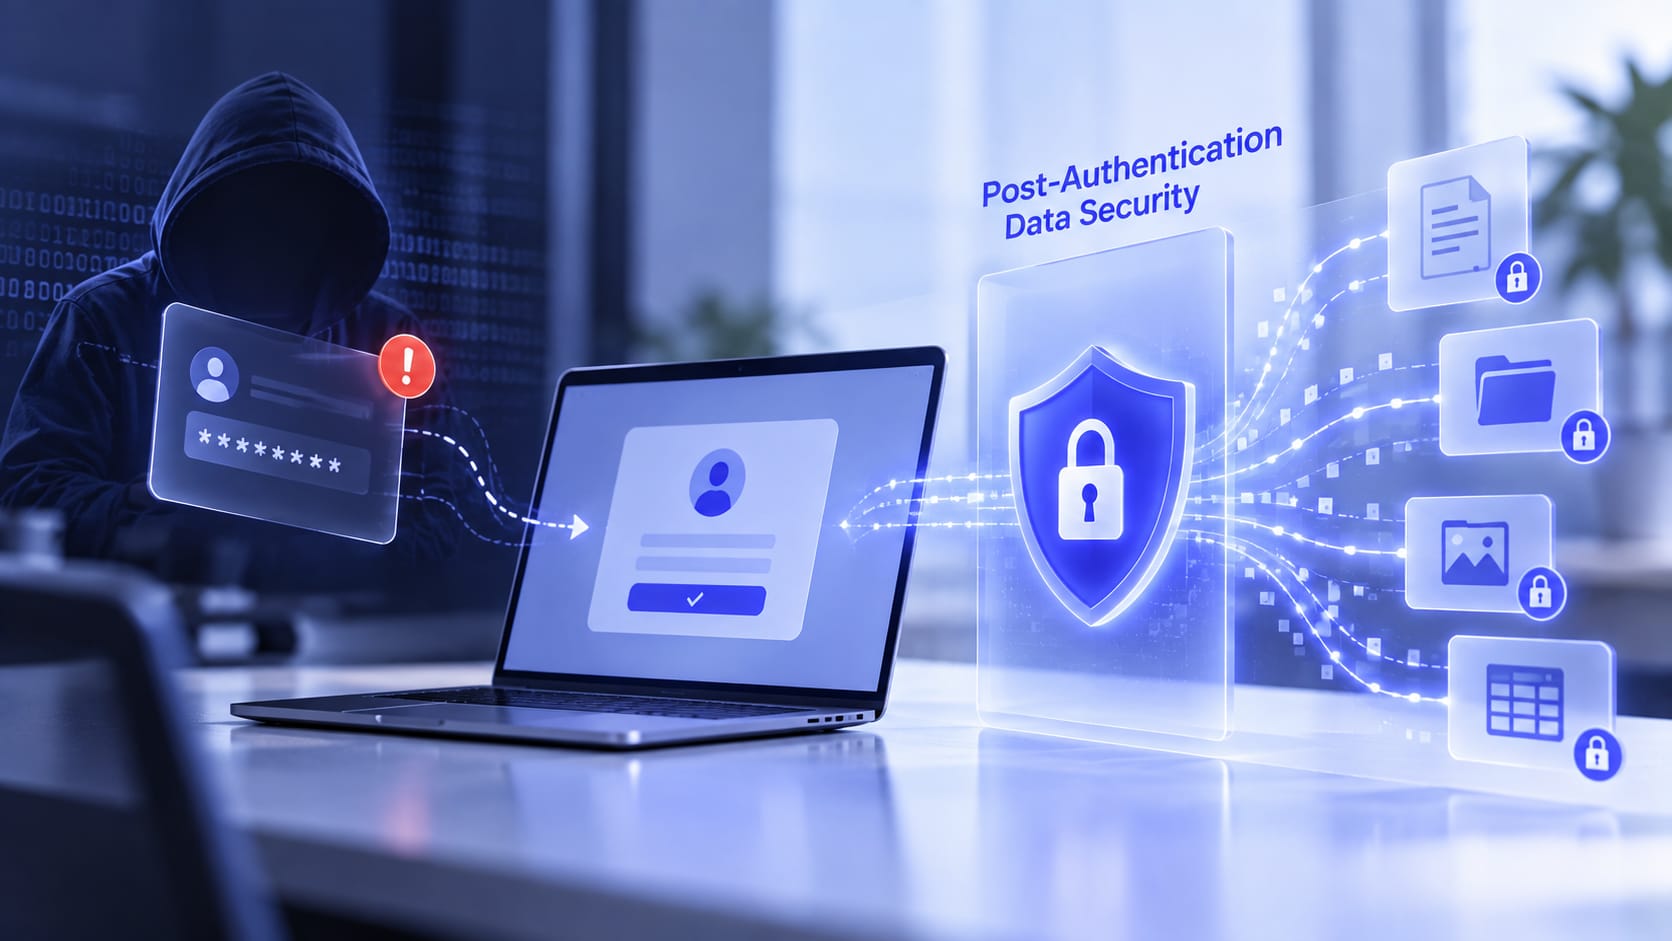
Once those credentials are harvested and used, whether the initial access came through a vulnerability, a phishing email, a compromised third party, or a malicious insider, every access-layer control stands down by design. The attacker is authenticated. Every protection was built to trust authenticated sessions.
What happens to the data in that authenticated session is the question the current security model does not answer.
What Post-Access Data Security Answers
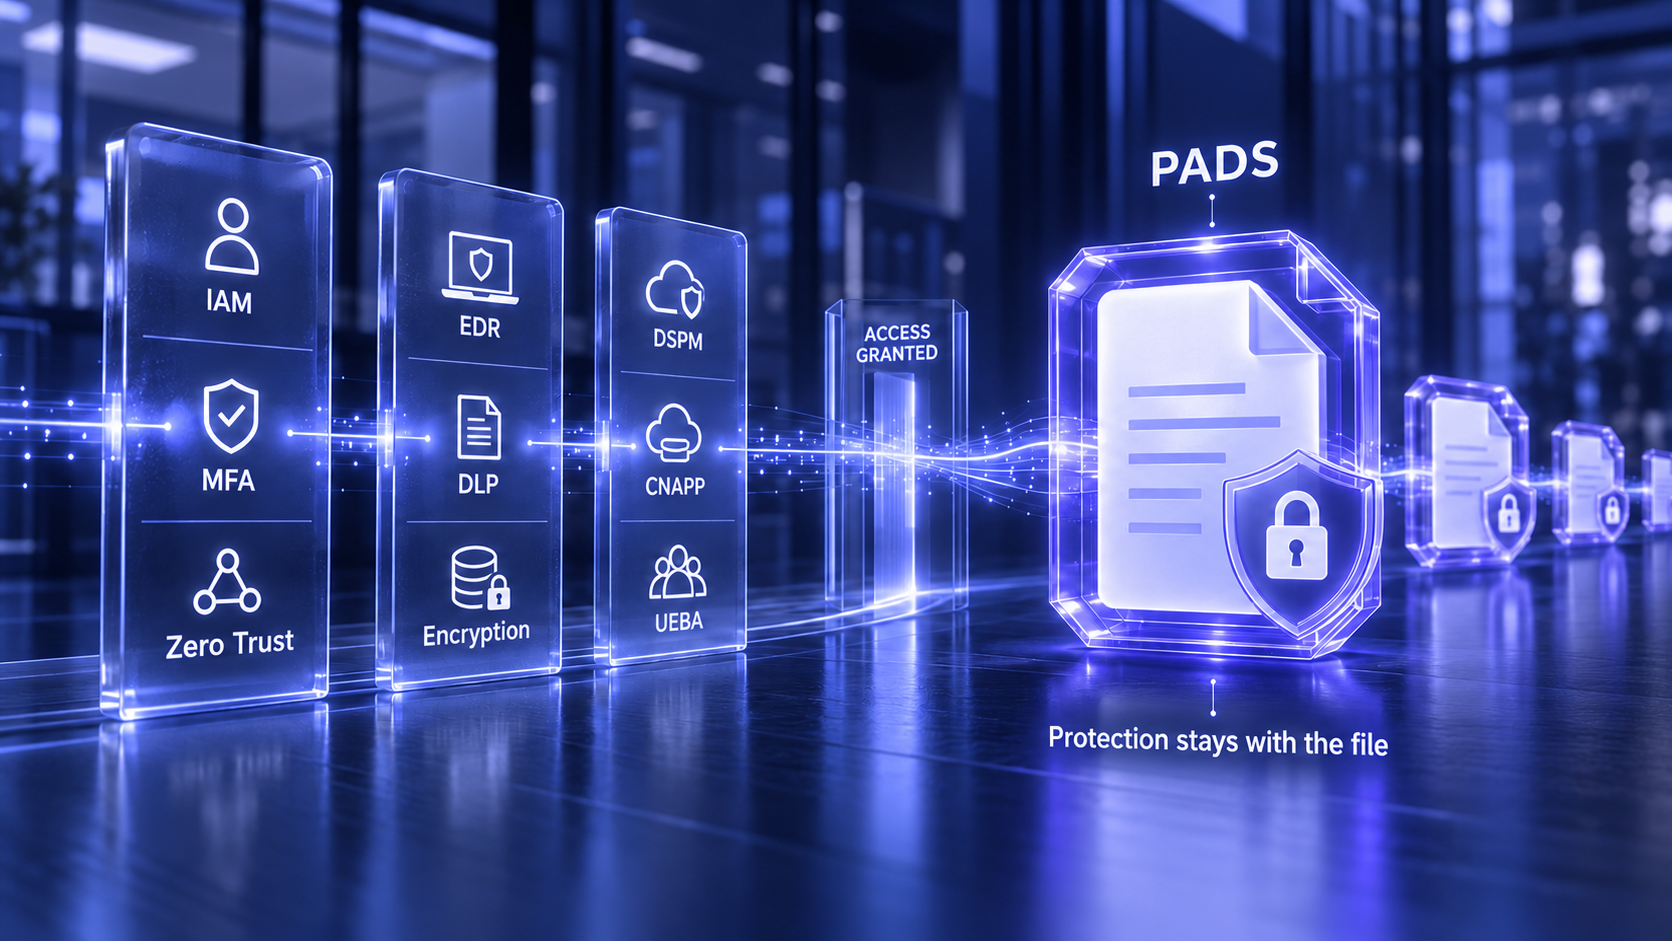
Post-Access Data Security (PADS), shifts the protection boundary from the session to the file itself.
Under a PADS model, file-layer encryption travels with the data. It persists through authenticated sessions. It renders files unreadable to anyone who cannot meet authorization requirements at the moment of use, regardless of the credentials used to reach them. An attacker who authenticates with stolen credentials and exfiltrates files obtains ciphertext. The files are useless regardless of how the authentication succeeded. The breach still occurs. The harm does not.
This is not a theoretical control. The regulatory framework already recognizes it. GDPR Article 34 exempts organizations from breach notification when data is encrypted and rendered unintelligible to unauthorized parties. HIPAA’s Breach Notification Safe Harbor treats encrypted breached data as a non-reportable event. California, New York, and most state breach notification statutes include explicit encryption safe harbors.
The regulatory system already knows that file-layer protection changes the legal character of a breach. It is the security model that hasn’t caught up.
The Strategic Implication
The 2026 DBIR’s remediation data is not an argument for abandoning access-layer security. MFA matters. Patching matters. Credential hygiene matters. The DBIR is right to recommend them.
The remediation data is an argument for accepting a fundamental truth: the access-layer perimeter cannot be fully secured at the scale and speed modern organizations require. The treadmill will keep accelerating. The attack surface will keep expanding. The remediation gap will persist regardless of investment.
Given that reality, protecting the data itself, independently of whether the perimeter holds, is not a supplementary control. It is the only control that remains effective when everything else has reached its theoretical limit.
Security teams fully remediated only 26% of critical vulnerabilities last year. The data inside those unpatched systems needs to protect itself.
That is what Post-Access Data Security delivers.
Christopher A. Dailey, Esq. is a licensed attorney and Chief Revenue Officer of PostAuth, Inc. The full academic treatment of the Post-Access Data Security Duty as an emerging legal standard is available on SSRN: https://papers.ssrn.com/sol3/papers.cfm?abstract_id=6750099